In this article 5 sections
The proof gap
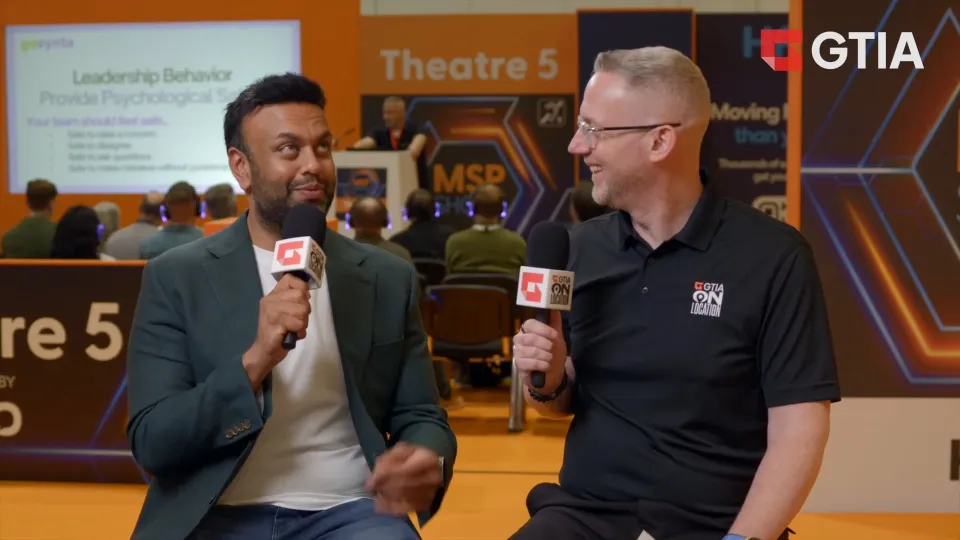
Olivia Staples, junior programme manager for techUK’s cyber resilience programme, interviews Mit Patel, founder and CEO of Assurix, for techUK’s Talking 5 series. The 12-minute episode looks at the gap between what MSPs claim about their security and what they can prove.
Mit, who ran an MSP for about 20 years, calls this the proof gap. Most of what MSPs show is point-in-time evidence. He compares it to an MOT. The car passes on the day, but that says nothing about the brakes or tyres 100 days later. Two MSPs can hold the same certificate and vary wildly inside. Ask MSPs whether they have taken on a client and been shocked by missing basics such as backups or MFA, and nearly all will say yes.
SMEs also struggle to choose between providers who sound the same, so the decision often defaults to price. Lower-priced providers often can’t put enough time into each client. It isn’t malicious, but corners get cut.
Why a yearly certificate is not enough
A yearly assessment, Mit says, leaves 364 days when nobody knows the real posture. ISO 27001 adds another problem. Each company decides which risks it accepts. His example is three friends racing in the rain, one on bald tyres who accepts the risk fully. Two MSPs can both hold ISO, and there is no external way to check they follow the processes.
What insurers and Assurix are doing
Insurers are moving towards continuous assurance. Some ask for software on devices or networks to see live telemetry. Mit says Assurix was born out of MSPs being fed up with being compared to MSPs that aren’t as good. It measures security posture aligned to the NCSC Cyber Assessment Framework, and operational maturity through the remote management and ticketing tools MSPs already use. If an MSP falls out of compliance, it has 30 days to fix it. If it doesn’t, the Trustmark is suspended publicly.
What MSPs should do now
Mit’s view is that “trust has to be earned with continuous proof”. He encourages MSPs to adopt a framework that gives them that proof. MSPs have access to clients’ email, files, security tools and backups. Insurers are wary of that single point of access, and MSP premiums are rising. Because MSPs “hold the keys to the kingdom”, one breach can affect many people.
Common questions
What is the proof gap?
The gap between what an MSP says about its security and what it can show. Most MSPs rely on point-in-time evidence that says little about the months in between.
Why is ISO 27001 alone not proof, in Mit’s view?
Each company sets its own risk tolerance, so two ISO holders can make very different choices. There is also no external way to check that the stated processes are followed.
How are insurers changing?
They are moving towards continuous assurance, and some ask for software that gives them live telemetry. They are also wary of the access MSPs hold to many clients.
What is the Assurix Trustmark?
The live trustmark for MSPs. Assurix independently assesses 59 controls: 40 security controls aligned to NCSC CAF 4.0 and 19 operational controls built for MSPs. Live-measured controls are checked every six hours and the rest on a set cycle. An Assurix assessor signs off. A failure left unfixed for 30 days suspends the Trustmark publicly.