In this article 8 sections
Cyber Essentials is the UK government-backed cyber security certificate, and businesses choosing an MSP are told to look for it. This guide covers what it tests, how Cyber Essentials and Cyber Essentials Plus differ, what the 2026 requirements mean for an MSP’s own estate, and where the certificate stops.
What Cyber Essentials is
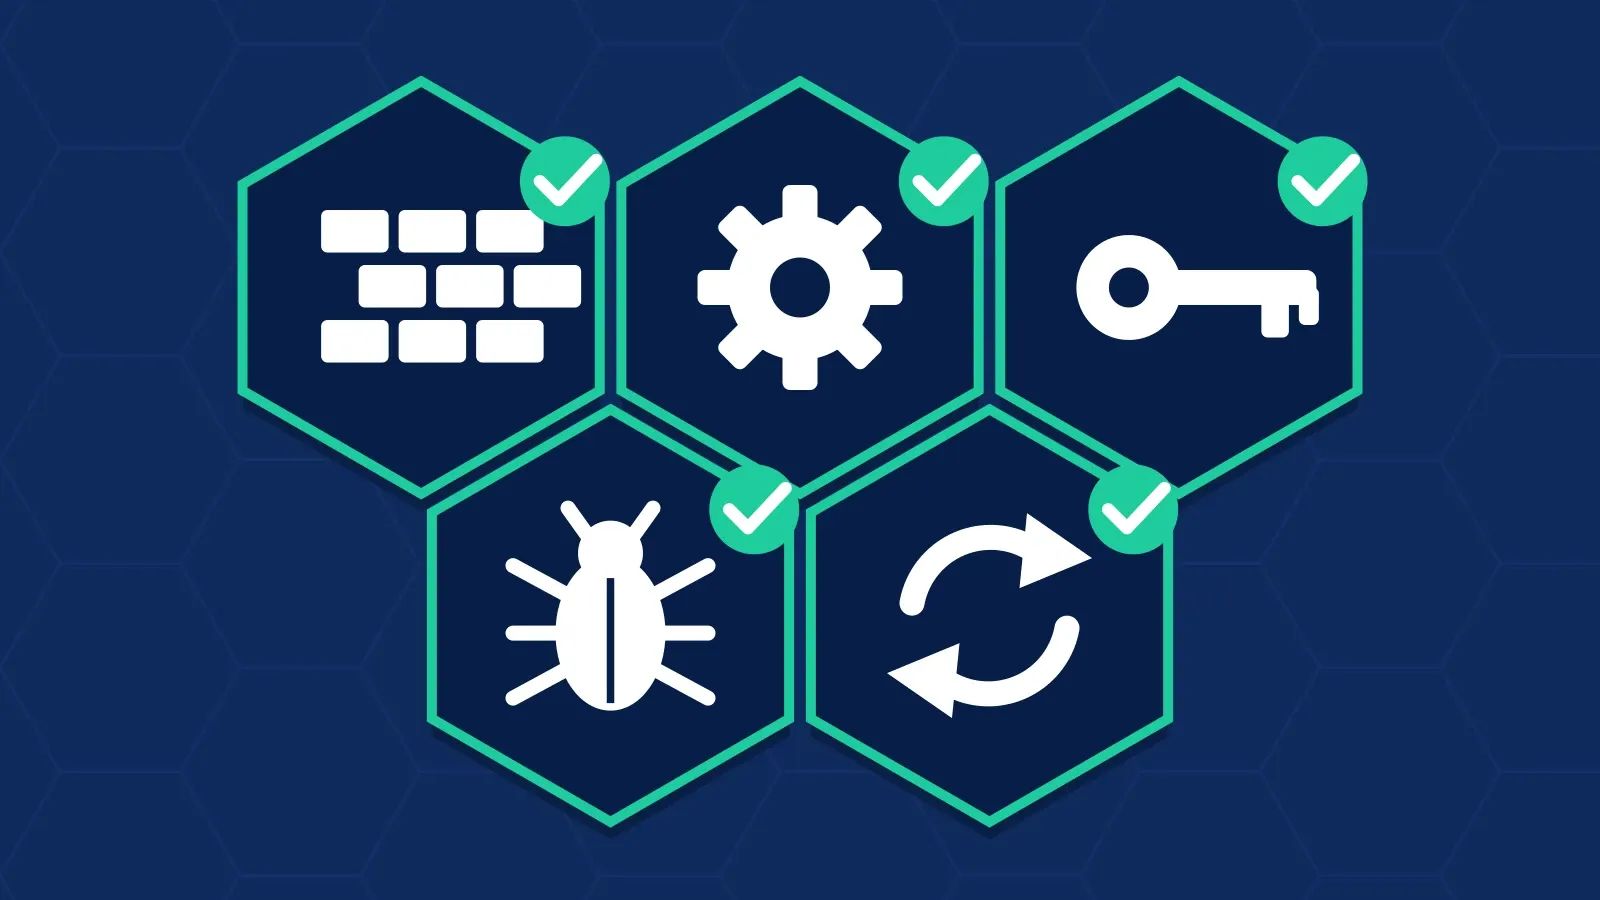
The NCSC calls Cyber Essentials “the minimum standard of cyber security recommended by the Government for organisations of all sizes”. The scheme is “aligned to five technical controls designed to prevent the most common internet based cyber security threats” (NCSC, Cyber Essentials).
IASME runs certification as the NCSC’s official Cyber Essentials Delivery Partner. You register and pay through IASME, then complete a verified self-assessment, on your own or with help from a Certification Body licensed by IASME. A board member or equivalent signs off the answers, and an assessor marks them (NCSC, Cyber Essentials).
Why it matters to an MSP
- Businesses are told to look for it. NCSC guidance for businesses choosing an MSP has a section headed “Certifications matter”. It tells them to use MSPs “with recognised certifications such as Cyber Essentials Plus”, because a certified MSP “acts as a quality and trust indicator” (NCSC, Choosing a managed service provider).
- Supply chains ask for it. The NCSC says “a growing number of organisations require suppliers to be certified to bid for work” (NCSC, Cyber Essentials), and it calls on large organisations to require Cyber Essentials across their supply chain (NCSC, Secure your supply chain).
- It cuts questionnaire time. Suppliers “can also use Cyber Essentials as evidence across their customer base, reducing the time spent filling out duplicative questionnaires” (NCSC, Secure your supply chain).
- Anyone can check it. Every current certificate is listed on IASME’s certificate search, which the NCSC links from its Cyber Essentials page (NCSC, Cyber Essentials).
The five technical controls
| Control | What the NCSC says it does |
|---|---|
| Firewalls | Create a security filter between the internet and your network |
| Secure configuration | Set up computers securely to minimise ways that a cyber-criminal can find a way in |
| Security update management | Prevent cyber criminals using vulnerabilities they find in software as an access point to your systems |
| User access control | Control who can access your data and services and what level of access they have |
| Malware protection | Identify and immobilise viruses or other malicious software before it has a chance to cause harm |
Source: NCSC, Cyber Essentials.
What the 2026 requirements mean for an MSP’s own estate
The requirements for each control are set out in Requirements for IT infrastructure. The current version, v3.3, took effect on 27 April 2026 (NCSC, Cyber Essentials resources). Five points from it land hard on an MSP (NCSC, Requirements for IT infrastructure v3.3):
- Cloud services are in scope. “Cloud services cannot be excluded from scope.” For most MSPs that takes in Microsoft 365 and any cloud-hosted tools you run clients from.
- End-user devices are in scope. “A scope that doesn’t include end-user devices isn’t acceptable.”
- MFA on every cloud service. “Authentication to cloud services must always use MFA.”
- 14 days for serious updates. Updates that fix vulnerabilities the vendor rates “critical” or “high risk” must be applied within 14 days of release.
- What’s new in v3.3. A definition of cloud services, FIDO2 in the definition of passwordless authentication, and more weight on backing up data.
Cyber Essentials or Cyber Essentials Plus?
Both assess the same five controls. Cyber Essentials Plus “goes a step further by independently testing your systems to verify that those controls are working in practice” (NCSC, Cyber Essentials).
| Cyber Essentials | Cyber Essentials Plus | |
|---|---|---|
| Controls | The same five | The same five |
| How it is checked | Verified self-assessment, marked by an assessor | The same, plus independent technical testing |
| Price | Tiered by organisation size, from £320 plus VAT | Quoted, by the size and complexity of your network |
Plus builds on the basic certificate. Its assessor checks that the Plus scope matches the scope of “the valid Cyber Essentials self-assessment certificate”, and any single failed test fails the whole assessment (NCSC, Cyber Essentials Plus test specification).
The NCSC’s MSP guidance names Cyber Essentials Plus, so Plus is the level to aim for. What Cyber Essentials Plus actually means for MSPs covers the audit, the timeline and what to fix first.
Renewal
A certificate lasts a year, and you renew it every year to stay certified. In between, it shows the position on the day you were assessed, not today.
Where Cyber Essentials stops
Its five controls are technical. They don’t cover board ownership of cyber risk, your suppliers, security monitoring or how you respond to an incident. Those sit in the NCSC Cyber Assessment Framework, which our guide to NCSC CAF 4.0 for MSPs explains.
A certificate proves a date. Assurix proves today.
How Assurix builds on Cyber Essentials
Keep the certificate. It is a good foundation, and the NCSC tells businesses that certifications matter. Assurix builds on it.
Assurix independently assesses 59 controls: 40 security controls aligned to NCSC CAF 4.0, and 19 operational controls built for MSPs. The security controls cover the ground Cyber Essentials leaves out, from supplier risk to acting on alerts and practising your incident response.
- Start from what you have. Launchpad reads your existing policies and documents, and Rosie maps them to the controls. Holding Cyber Essentials helps.
- Stay current between renewals. Live-measured controls are checked every six hours from your own tools, and the rest on a set cycle. An Assurix assessor signs off.
- Be held to it. A failure opens a 30-day window to fix it. If it isn’t fixed, the Trustmark is suspended publicly.
- Let prospects check. The result sits on your Trust Portal, a link any prospect can open.
You work from 2 hours a week, at the pace you set.